What Is a Salt and Why Does It Matter for Encryption?
The word "salt" appears in almost every discussion of password security, yet it is often confused with encryption itself. A salt is a small piece of random data added to a password before it is hashed, so identical passwords stop producing identical results.
This guide explains what a salt is, why it defeats precomputed attacks, and where salts appear in the tools you use every day.
PAGE CONTENT
- What a Salt Is
- How Salting Defeats Precomputed Attacks
- Where Salts Appear
- Protect Files with Safe Disk
- What Salts Do Not Fix
- FAQs About Salts and Hashing
- Back Up Windows Before You Change Settings
What a Salt Is
- It is random data. A salt is a unique value generated for each stored password.
- It is not secret. Salts are stored next to the hash, because the system needs them to check a login.
- It is added before hashing. The password and salt are combined, then hashed into a fixed-length value.
- It changes the output. The same password with a different salt produces a completely different hash.
- It is not encryption. A salt does not hide data; it makes hashing unique and slower to attack.
Think of a salt as a serial number that turns one shared recipe into a unique dish for every account.
How Salting Defeats Precomputed Attacks
- Rainbow tables break without a salt. Precomputed lists of common password hashes are useless when each entry has its own salt.
- Identical passwords stop matching. Two users with the same password no longer share a hash.
- Attackers must work per account. Cracking one password no longer reveals the rest.
- Attack cost rises sharply. Brute force must be repeated for every salt, which multiplies the work.
- Slow hashing adds more. Modern systems combine salts with deliberately slow algorithms to make guessing expensive.
The salt does not make a weak password strong, but it removes the shortcuts attackers relied on for decades.
Where Salts Appear
- Password storage. Every properly built login system salts each stored password.
- Password managers. The vault key is derived from your master password with a salt and many rounds of hashing.
- Disk encryption. Full-disk tools derive keys through salted hashing so the same password yields different keys.
- Encrypted containers. Container headers store a salt plus other parameters needed to derive the key.
- Backup tools. Encrypted backups derive their keys the same way, which is why the header matters.
In short, any system that turns a password into a key or a stored hash will use a salt somewhere. The algorithm behind that step is covered in What Is AES-256 Encryption.
Protect Files with Safe Disk
Qiling Safe Disk derives its container key from your password with salted hashing and encrypts the data with AES-256. Download and install it first.
Step 1. Open Qiling Safe Disk and click Create to make a new container.
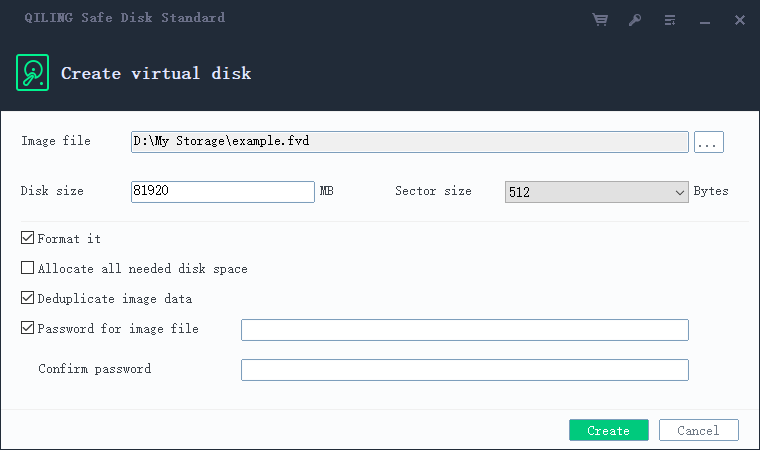
Step 2. Set the size, choose AES-256, and set a long, unique password.
Step 3. Click Create and wait for the container to be written.
Step 4. Mount the container and copy the files you want to protect inside it.
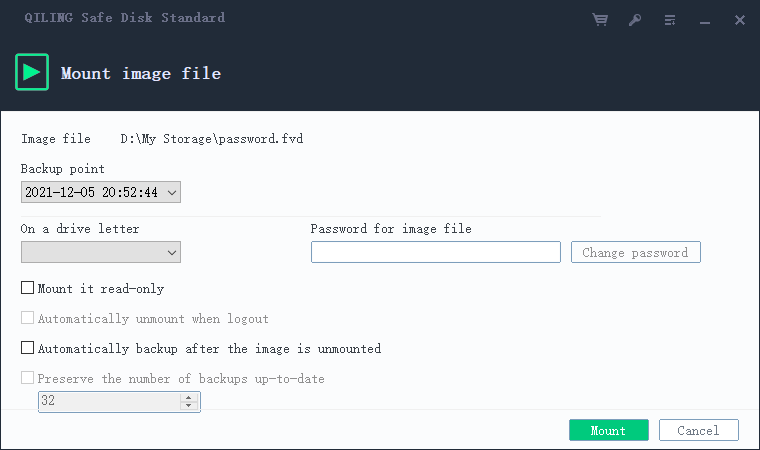
Step 5. Unmount when you are done so the container locks again.
What Salts Do Not Fix
- A weak password. A common password with a salt is still a common password.
- Reused passwords. One breach can still open other accounts if you repeat a password.
- Malware on the device. A keylogger captures the password before hashing ever happens.
- An unlocked container. A mounted volume is readable regardless of how the key was derived.
- Missing backups. Salting protects credentials, not files you never copied.
Salts harden the conversion step. Choosing long, unique passwords and keeping containers unmounted is what protects the data itself. For help storing passwords safely, see How to Encrypt Passwords and Credentials.
FAQs About Salts and Hashing
Is a salt the same as a key?
No. A salt is public random data used while deriving a key; the key itself stays secret.
Can a salt be reused?
It should be unique per password. Reusing one salt across a whole database restores the shortcuts salting was meant to remove.
Does adding a salt make hashing reversible?
No. Hashing is one-way; the salt does not make it decryptable.
Is a salted password safe if a database leaks?
Much safer than an unsalted one, but the strength of the original password still decides how long it survives.
Do I need to set a salt myself?
No. Good software generates and stores it automatically; your job is to choose a strong password.
Back Up Windows Before You Change Settings
Before installing security software or changing storage, create a full Windows backup. Qiling Disk Master creates a system image you can restore from.
Step 1. Open Qiling Disk Master and select System Backup to include Windows and the boot partitions.
Step 2. Save the image to a drive other than the Windows disk and start the backup.
Step 3. If a change causes issues, restore from the image to return Windows to its working state.
Conclusion
A salt is unique random data added to a password before hashing, so identical passwords produce different stored values and precomputed tables stop working. It is not encryption and not a secret; it is a shortcut-killer that forces an attacker to work account by account. Password managers, disk encryption tools, and encrypted containers all use salted hashing to turn a password into a key. Qiling Safe Disk does the same and then encrypts your files with AES-256. A salt cannot rescue a weak or reused password, so choose long unique passwords and keep the container unmounted when idle.
For more on how encryption protects files, see What Is a Virtual Encrypted Drive, How to Back Up an Encrypted Drive, Best Encryption Algorithm for Files, and How to Use Qiling Safe Disk.
Related Articles
- What Is a Keyfile and How Does It Work?
A keyfile adds a second secret to an encrypted drive. Learn what it is, how it combines with a password, and how to store it. - Is an Encrypted Drive Safe from Hackers?
Encryption stops most attackers, but not all of them. See what it defends against and where the gaps are. - What Is a Key Derivation Function?
A key derivation function turns a password into an encryption key. Learn how PBKDF2, scrypt, and Argon2 slow down guessing attacks. - What Is an Encrypted Container File?
A container keeps many files inside a single locked archive. Learn how it works and when to use one. - Does Encryption Slow Down a Disk?
Worried encryption will make your PC crawl? See how much speed modern hardware encryption actually costs.
Products
Articles & Tutorials
- Data Recovery
- Data Backup
- File Recovery
- File Backup
- System Backup and Restore
- Disk and Partition Clone
- Technical articles
- Mobile articles
- Disk Master Help
- Windows Data Recovery Tutorials
- Windows Secure Delete Tutorials
- Windows Partition Management Tutorials
- Windows File Backup and Restore Tutorials
- Windows System Backup and Restore Tutorials
- Windows Disk Backup and Restore Tutorials
- Windows Clone Tutorials