What Is a TPM and How Does It Help Encryption?
A trusted platform module is a small chip on the motherboard that stores secrets and checks that a computer started the way it should. It is the reason many laptops can encrypt a disk without asking for a password at every boot.
This guide explains what a TPM does, how it works with disk encryption, what it cannot protect, and when to combine it with password-based containers.
PAGE CONTENT
- What a TPM Does
- How a TPM Supports Encryption
- Keys, Sealing, and Measured Boot
- Add Container Encryption with Safe Disk
- Where TPM Protection Stops
- FAQs About TPMs and Encryption
- Back Up Windows Before You Change Settings
What a TPM Does
- It stores keys. Private keys are generated inside the chip and normally never leave it.
- It measures the boot process. Hashes of firmware and boot files are recorded in registers.
- It seals secrets. A key can be released only when the measurements match the expected values.
- It resists tampering. Opening or probing the chip can destroy the keys it holds.
- It is standardised. The same commands work across vendors, which is why operating systems support it.
A TPM is not a disk or a backup. It is a small vault plus a notary that confirms how the machine started.
How a TPM Supports Encryption
- It unlocks a disk key. The encryption key is sealed to the chip, so it is only released on the right machine.
- It enables silent boot. With a TPM, a laptop can start without typing a password every time.
- It detects firmware changes. A modified bootloader changes the measurements, so the key is withheld.
- It pairs with a PIN. Adding a startup PIN means a stolen laptop cannot boot even on the right hardware.
- It supports recovery keys. When sealing fails, a printed or escrowed recovery key restores access.
This is the mechanism behind most business laptop encryption, described in What Is Full Disk Encryption.
Keys, Sealing, and Measured Boot
- Endorsement key. A unique identity burned into the chip at manufacture.
- Storage root key. The parent key that protects everything else stored in the TPM.
- Platform configuration registers. The hash chain that records firmware, bootloader, and kernel.
- Sealed blobs. Data encrypted so it can be opened only under a specific measurement set.
- Attestation. A signed report that lets a server verify a machine's boot state.
The disk key itself is still a symmetric key used by a cipher such as What Is AES-256 Encryption; the TPM only guards how that key is released.
Add Container Encryption with Safe Disk
Qiling Safe Disk protects individual files with a password-based AES-256 container, which covers the case a TPM cannot: data copied to another machine. Download and install it first.
Step 1. Open Qiling Safe Disk and click Create to make a new container.
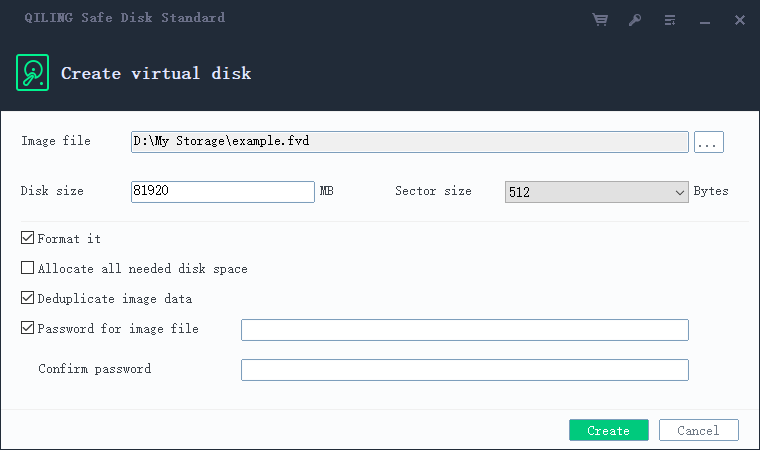
Step 2. Set the size, choose AES-256, and set a long, unique password.
Step 3. Click Create and wait while the container is written.
Step 4. Mount the container and copy the files you want to protect inside it.
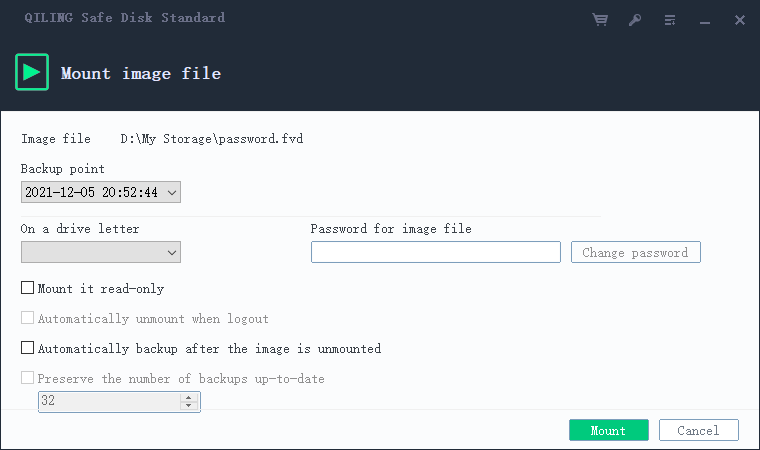
Step 5. Unmount when you are done so the container locks again.
Where TPM Protection Stops
- A running system is open. Once the machine boots, malware can read whatever the user can read.
- Copied files leave the seal. A file moved to another PC is no longer protected by that TPM.
- Weak login passwords still matter. The TPM unlocks the disk, not the user account.
- Firmware attacks exist. A compromised boot chain can measure as valid if the attacker controls the code.
- Recovery keys can leak. A recovery key stored in a public folder defeats the whole design.
A TPM protects a disk at rest on its own hardware. It does not protect files in transit, in the cloud, or in an email attachment.
FAQs About TPMs and Encryption
Do I need a TPM to encrypt a drive?
No. Password-based container encryption works without one, which is useful on older machines.
Does a TPM replace my password?
It replaces the disk password at boot, but your Windows login still controls access to the account.
What happens if the motherboard dies?
The sealed key is lost with the chip, so you need the recovery key or a backup to read the disk.
Is a TPM 2.0 better than 1.2?
Yes. Version 2.0 supports modern algorithms and is what current operating systems expect.
Can a TPM protect files on a USB drive?
Not directly. Use an encrypted container with a password instead, so the file stays protected on any PC.
Back Up Windows Before You Change Settings
Before installing security software or changing storage, create a full Windows backup. Qiling Disk Master creates a system image you can restore from.
Step 1. Open Qiling Disk Master and select System Backup to include Windows and the boot partitions.
Step 2. Save the image to a drive other than the Windows disk and start the backup.
Step 3. If a change causes issues, restore from the image to return Windows to its working state.
Conclusion
A TPM is a chip that stores keys and records how a computer starts, so a disk key can be released only on the expected hardware and boot path. It makes full-disk encryption convenient and blocks simple disk removal, but it does not protect files once the system is running, copied, or emailed. Add a startup PIN and keep the recovery key somewhere safe. For files that travel, use a password-based AES-256 container such as Qiling Safe Disk, which stays locked on any machine.
For more on how encryption protects files, see What Is a Virtual Encrypted Drive, How to Back Up an Encrypted Drive, Best Encryption Algorithm for Files, and How to Use Qiling Safe Disk.
Related Articles
- Self-Encrypting Drive vs Software Encryption
The drive can lock itself, or the software can. Compare the two approaches and their trade-offs. - What Is a Keyfile and How Does It Work?
A keyfile adds a second secret to an encrypted drive. Learn what it is, how it combines with a password, and how to store it. - What Is a Recovery Key and Where Should You Keep It?
Lose the recovery key and the data is gone. Learn what a recovery key is and where to store it safely. - What Is a Cold Boot Attack and How Do You Prevent It?
A cold boot attack reads the drive key out of memory. See how it works and what limits the risk. - What Is Secure Boot and How Does It Help Encryption?
Secure Boot checks the boot path before your disk unlocks. See how it supports encryption and where its help stops.
Products
Articles & Tutorials
- Data Recovery
- Data Backup
- File Recovery
- File Backup
- System Backup and Restore
- Disk and Partition Clone
- Technical articles
- Mobile articles
- Disk Master Help
- Windows Data Recovery Tutorials
- Windows Secure Delete Tutorials
- Windows Partition Management Tutorials
- Windows File Backup and Restore Tutorials
- Windows System Backup and Restore Tutorials
- Windows Disk Backup and Restore Tutorials
- Windows Clone Tutorials