What Is Secure Boot and How Does It Help Encryption?
Disk encryption has one obvious weak moment: the point where you type the password and the drive unlocks. Whatever runs before that moment can see everything you type. Secure Boot exists to make that pre-boot stage harder to tamper with.
This article explains what Secure Boot checks, how it works with full disk encryption and a TPM, and what it still cannot do.
PAGE CONTENT
- What Secure Boot Is
- How It Protects the Boot Chain
- Where a TPM Fits In
- Add Container Encryption with Safe Disk
- Where Secure Boot Stops
- FAQs About Secure Boot and Encryption
- Back Up Windows Before You Change Settings
What Secure Boot Is
- It is a firmware feature. Secure Boot lives in the UEFI firmware, not in Windows.
- It checks signatures. Each boot component must be signed by a key the firmware trusts.
- Keys sit in firmware. The trusted list is stored in the machine, not on the disk.
- Unsigned code is refused. A modified bootloader stops the machine instead of running.
- It is a setting you can see. The firmware setup screen shows whether Secure Boot is on.
In short, Secure Boot makes sure the machine starts the software the manufacturer expected and nothing else.
How It Protects the Boot Chain
- Encryption unlocks at boot. The key is released by early boot code, before Windows is fully running.
- A tampered loader could capture the password. Malicious pre-boot code can log every keystroke.
- Secure Boot blocks that path. An unsigned loader never gets the chance to run.
- It covers the pre-boot stage. That is exactly the window encryption cannot defend on its own.
- It needs a recovery plan. A firmware change can lock you out, so keep recovery media ready.
This is the practical link between the two features. What Is Full Disk Encryption? explains the key side of the same moment.
Where a TPM Fits In
- The TPM measures the boot path. It records hashes of the firmware and boot components.
- Keys can be sealed to those values. The disk key is released only when the measurements match.
- Secure Boot feeds the measurements. Its checks are what the TPM ends up recording.
- A changed bootloader breaks the match. The key stays sealed and the drive stays locked.
- You still need a recovery key. Hardware changes can also break the match, so store the key elsewhere.
The chip and the firmware setting work as a pair, which is why What Is a TPM and How Does It Help Encryption? is the natural next read.
Add Container Encryption with Safe Disk
Secure Boot protects how the machine starts; Qiling Safe Disk protects the files themselves, so a locked container still needs a password after Windows is running. Download and install it first.
Step 1. Open Qiling Safe Disk and click Create to make a new container.
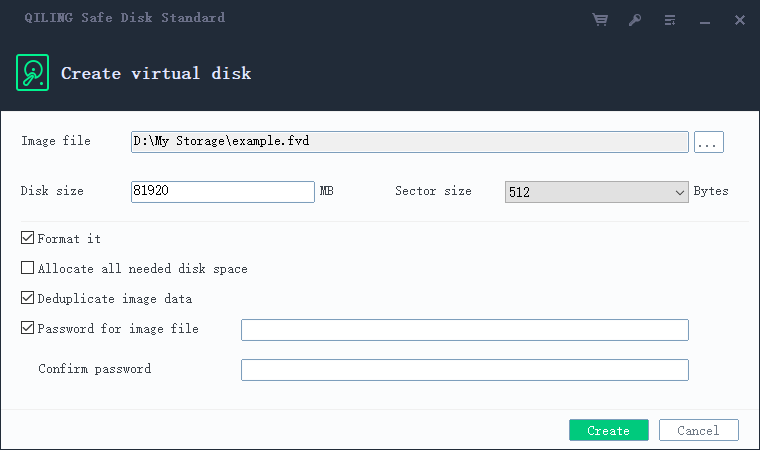
Step 2. Set the size, choose AES-256, and use a long password you keep apart from the drive password.
Step 3. Click Create and wait for the container to be written.
Step 4. Mount the container and move contracts, payroll files, or research notes inside it, so they stay protected even on a machine that is already unlocked.
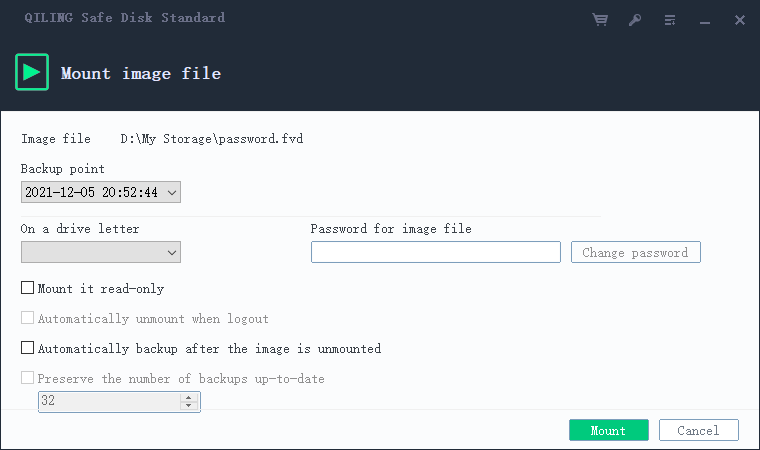
Step 5. Unmount when you finish so the container locks again.
Where Secure Boot Stops
- It does not encrypt anything. A stolen drive is still readable if the disk itself is not encrypted.
- It does not watch Windows. Malware that loads after boot is outside its scope.
- It does not stop a logged-in attacker. Once you unlock, files open normally.
- It can block useful tools. Some recovery and dual-boot setups need it turned off or re-signed.
- Firmware can have flaws. Bugs and leaked signing keys have undermined it before.
Secure Boot is one link in a chain, not the whole chain. Encryption, strong passwords, and a stored recovery key do the rest.
FAQs About Secure Boot and Encryption
Do I need Secure Boot if my drive is encrypted?
It is strongly recommended. Encryption protects a powered-off drive; Secure Boot protects the moment you unlock it.
Does Secure Boot encrypt my files?
No. It only verifies boot code. Data protection still comes from disk and container encryption.
Will turning it off break my encrypted drive?
It can. If the disk key is sealed to boot measurements, disabling Secure Boot changes them and may require the recovery key.
How do I check whether it is on?
Open the firmware settings, or run the Windows system information tool and look at the Secure Boot state.
Is it enough on its own?
No. Treat it as a base layer and combine it with full disk encryption and encrypted containers.
Back Up Windows Before You Change Settings
Before installing security software or changing storage, create a full Windows backup. Qiling Disk Master creates a system image you can restore from.
Step 1. Open Qiling Disk Master and select System Backup to include Windows and the boot partitions.
Step 2. Save the image to a drive other than the Windows disk and start the backup.
Step 3. If a change causes issues, restore from the image to return Windows to its working state.
Conclusion
Secure Boot is a firmware check that only signed boot code runs, which matters because disk encryption unlocks its key at exactly that moment. Together with a TPM, it seals the key to the measurements of a clean boot path, so a tampered loader cannot capture your password. It does not encrypt data, does not watch Windows after startup, and cannot help once you are logged in. Use it as the base layer, add full disk encryption for the drive, and keep sensitive files in an AES-256 container such as Qiling Safe Disk. Store the recovery key somewhere other than the machine.
For more on how encryption layers fit together, see What Is a Virtual Encrypted Drive?, How to Back Up an Encrypted Drive, How to Protect a Laptop When Traveling, and How to Use Qiling Safe Disk.
Related Articles
- Self-Encrypting Drive vs Software Encryption
Hardware and software encryption handle keys very differently. See which one fits the way you work. - Is an Encrypted Drive Safe from Hackers?
Encryption stops most attackers, but not all of them. See what it defends against and where the gaps are. - What Is a Recovery Key and Where to Keep It?
A recovery key is your way back into an encrypted drive. Learn where to store it so it is never lost. - Encrypted Drive vs BitLocker: Which Should You Use?
Both protect a Windows drive, but they behave differently. See how they compare before you choose. - What Is a Keyfile and How Does It Work?
A keyfile adds a second factor to your password. Learn how it works and how to store it safely.
Products
Articles & Tutorials
- Data Recovery
- Data Backup
- File Recovery
- File Backup
- System Backup and Restore
- Disk and Partition Clone
- Technical articles
- Mobile articles
- Disk Master Help
- Windows Data Recovery Tutorials
- Windows Secure Delete Tutorials
- Windows Partition Management Tutorials
- Windows File Backup and Restore Tutorials
- Windows System Backup and Restore Tutorials
- Windows Disk Backup and Restore Tutorials
- Windows Clone Tutorials