Fix DRIVER_VERIFIER_DETECTED_VIOLATION (0xC4) in Windows 11
A blue screen with DRIVER_VERIFIER_DETECTED_VIOLATION usually appears in one of two situations: you turned on Driver Verifier while hunting another problem, or one of your drivers genuinely misbehaves and the tool caught it in the act.
Getting out of this stop code is often easier than most, because Driver Verifier is a setting you control. This guide shows how to read the parameters, escape a verifier boot loop, and then confirm whether the driver was actually faulty.
PAGE CONTENT
- What DRIVER_VERIFIER_DETECTED_VIOLATION Means
- First, Check Whether You Enabled Driver Verifier
- Get Out of the Boot Loop
- Read Parameter 1 to Identify the Fault
- Fix the Driver and Re-Test
- How to Use Driver Verifier Correctly
- FAQs About the 0xC4 Stop Code
- Back Up and Restore Windows with Qiling Disk Master
What DRIVER_VERIFIER_DETECTED_VIOLATION Means
The value 0x000000C4 is the general bug check code for fatal errors found by Driver Verifier. The full message explains the situation precisely:
A device driver attempting to corrupt the system has been caught. This is because the driver was specified in the registry as being suspect (by the administrator) and the kernel has enabled substantial checking of this driver.
Two details matter here. First, the driver was flagged as suspect before the crash, normally because someone enabled verification for it. Second, the kernel was applying extra checks, so it caught behaviour that would otherwise have gone unnoticed, or at least gone unnoticed until much later.
That is why this stop code is different from most blue screens. It is not usually a random failure. It is a test result: something in the driver was doing the wrong thing, under conditions that a normal Windows session never inspects.
- Note
- Driver Verifier reports a whole family of violations. Bug checks 0xC4, 0xC1, and 0xA are the ones you most commonly see when verification is active, so do not be surprised if the stop code changes between crashes while the setting remains on.
First, Check Whether You Enabled Driver Verifier
Before changing any driver, confirm the source of the crash.
Step 1. If Windows still starts, open an elevated Command Prompt and run verifier /querysettings. This lists the drivers currently being verified and the test types in use.
Step 2. If you see a list of third-party drivers, verification is active. If you applied the "standard settings" preset, every non-Microsoft driver is being checked, which means the crash may be a false alarm from a driver that was never the original problem.
Step 3. If Windows no longer starts, assume verification is active. You enabled it knowingly or followed a troubleshooting guide that told you to, and the stop code confirms the kernel is checking a driver.
Get Out of the Boot Loop
If every restart ends in another 0xC4, turn the setting off first and diagnose afterwards.
Step 1. Try to boot into Safe Mode. If Windows starts there, open an elevated Command Prompt and run:
verifier /reset
verifier /bootmode resetonbootfail
Step 2. Restart normally. The second command makes the system clear verifier settings automatically the next time a boot fails, which prevents the loop from returning.
Step 3. If you cannot reach Safe Mode, open the Recovery Environment. From the sign-in screen, hold Shift while selecting Restart. Then choose Troubleshoot > Advanced options > Command Prompt and run the two commands above.
Step 4. If Windows never reaches the recovery menu, force three failed startups. Start the PC and hold the power button for five to ten seconds while Windows is loading. Repeat twice; on the third attempt Windows should open the recovery options automatically.
Step 5. If BitLocker blocks the Command Prompt, you must supply the recovery key before those commands will run. See our guide on the BitLocker recovery key after a Windows update if the key is not where you expected.
Step 6. Alternatively, launch verifier, select Delete existing settings, and click Finish, then restart.
- Important
- Write down the drivers listed by
verifier /querysettingsbefore you reset it. That list is the shortlist of suspects, and once the settings are cleared you lose it.
Read Parameter 1 to Identify the Fault
Parameter 1 names the type of violation, and the remaining parameters change meaning depending on its value. These are the values you are most likely to meet:
| Parameter 1 | Meaning |
|---|---|
| 0x00 | The driver requested a zero-byte pool allocation. |
| 0x01 | The driver tried to allocate paged memory at an IRQL higher than APC_LEVEL. |
| 0x02 | The driver tried to allocate nonpaged memory at an IRQL higher than DISPATCH_LEVEL. |
| 0x10 | The driver freed an address that was never returned by an allocate call. |
| 0x11 / 0x12 | The driver freed paged or nonpaged pool at an IRQL that is too high. |
| 0x13 / 0x14 | A double free, meaning the driver released memory pool that had already been freed. |
| 0x15 | The pool being freed still contains an active timer. |
| 0x16 | The driver freed pool at a bad address or passed invalid parameters to a memory routine. |
| 0x17 | The pool being freed still contains an active ERESOURCE. |
| 0x30 / 0x31 | An invalid IRQL was passed when raising or lowering the IRQL. |
| 0x32 | A spin lock was released at an IRQL other than DISPATCH_LEVEL, often a double release. |
| 0x33 / 0x34 | A fast mutex was acquired or released at the wrong IRQL. |
| 0x35 / 0x36 | A spin lock or queued spin lock was released with an IRQL other than DISPATCH_LEVEL. |
Step 1. Note Parameter 1 from the blue screen or from the dump.
Step 2. If the value points at a double free or a freed address, look for a driver that manages its own buffers aggressively. Backup, encryption, and antivirus filter drivers are common sources, because they intercept file operations and allocate memory constantly.
Step 3. If the value points at an IRQL problem, suspect drivers that run code at high interrupt levels, such as audio, network, and storage drivers, especially older ones written before modern IRQL rules were enforced.
Step 4. Open the dump in a debugger and run !analyze -v. The module it names is the driver that failed the check, not necessarily the one you originally suspected.
Fix the Driver and Re-Test
Step 1. Update the named driver from the hardware or PC manufacturer. Many 0xC4 violations were fixed in later driver releases and never appear in normal use.
Step 2. If the crash started right after a driver update, roll that driver back instead.
Step 3. If no newer driver exists, remove the device or the application that installed the driver. An unmaintained product from an older Windows generation is a frequent offender.
Step 4. Remove duplicate filter drivers. Two backup, sync, encryption, or security products that both attach to the file system can cause exactly the kind of double free this stop code reports.
Step 5. Repair system files before retesting:
DISM /Online /Cleanup-Image /RestoreHealth
sfc /scannow
Step 6. Re-enable verification for the specific driver only, not for all drivers, and use the workload that originally failed. If the system stays stable, the violation is resolved.
How to Use Driver Verifier Correctly
Driver Verifier is a diagnostic tool, not a fix, and using it carelessly is the most common reason people end up with a machine that will not boot.
Step 1. Understand what you are enabling. The "standard settings" preset applies many tests to every non-Microsoft driver, which can produce crashes from drivers that were never causing your original problem.
Step 2. Create a full system backup before you enable it. A system image lets you return to a working state in minutes instead of rebuilding the machine.
Step 3. Make sure you still have a working way in. Confirm that you can reach Safe Mode, and keep your BitLocker recovery key accessible in case the recovery environment asks for it.
Step 4. Verify only the drivers you actually suspect, rather than the entire system.
Step 5. Set a fixed testing window. Verification slows the system down and can hide or create unrelated failures if left on for weeks.
Step 6. When you finish, always clear the settings with verifier /reset, then restart and confirm that verification is no longer listed by verifier /querysettings.
FAQs About the 0xC4 Stop Code
Did a driver really corrupt my system?
It means the kernel caught a driver doing something illegal while extra checks were enabled. Many violations are real but harmless in normal use, which is why 0xC4 often appears only after verification is turned on.
How do I turn Driver Verifier off if Windows will not boot?
Open the Recovery Environment, launch Command Prompt, and run verifier /reset followed by verifier /bootmode resetonbootfail. Both commands are needed to prevent the loop from returning.
Why did Driver Verifier cause a boot loop?
Because it applies extra checks to drivers that the system needs to load. If one of those drivers fails a check during startup, Windows bug checks before it can finish booting.
Can BitLocker block the recovery steps?
Yes. If the drive is encrypted, the recovery environment asks for the BitLocker recovery key before Command Prompt becomes available, so retrieve that key first.
Is it safe to leave Driver Verifier enabled?
No. It slows the system down and can trigger crashes from unrelated drivers. Enable it for a focused test, then clear the settings when the test is done.
Do I need to reinstall Windows?
Usually not. Clearing verifier settings is enough to boot again. Reinstalling is only worth considering if a driver you cannot remove keeps failing its checks.
Back Up and Restore Windows with Qiling Disk Master
Driver Verifier can leave a machine that will not boot, and driver rollbacks, BIOS updates, and hardware testing carry similar risks. Create a full system backup before you start. Qiling Disk Master handles both the backup and the restore.
Part 1: Create a Full System Backup
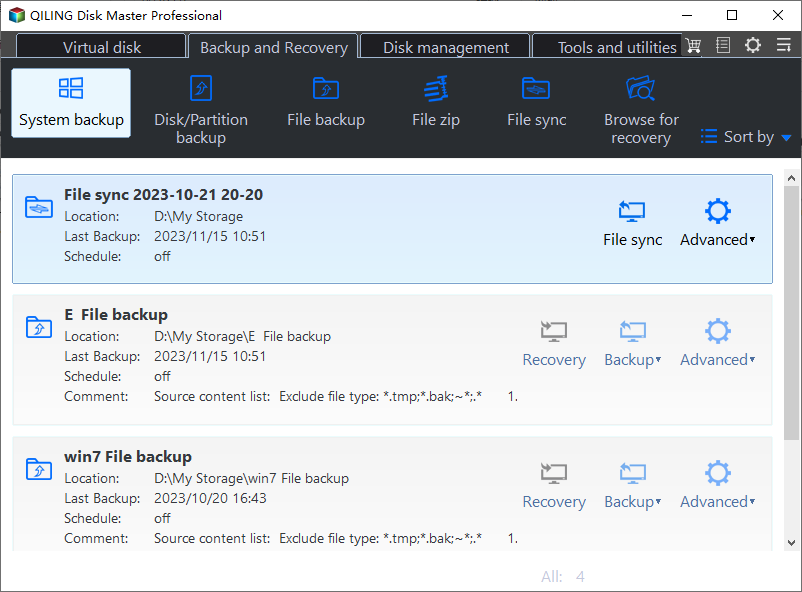
Step 1. Install and open Qiling Disk Master. On the home screen, open "Backup and Recovery" and choose "System Backup". This option automatically includes Windows and the hidden boot partitions, so you do not have to select them one by one.
Step 2. Check the source. The disk where Windows is installed and its system partitions are already ticked for you. If you only need your personal documents, run a separate "File Backup" task instead.

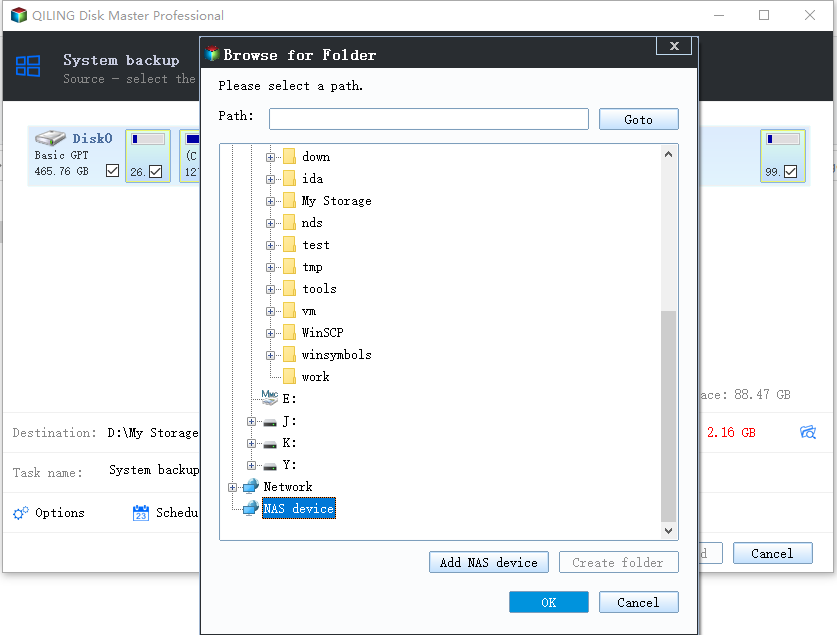
Step 3. Click the destination box and choose where the image should be saved. Use an external HDD or SSD, a NAS, or any drive other than the one Windows is installed on, and make sure it has enough free space.
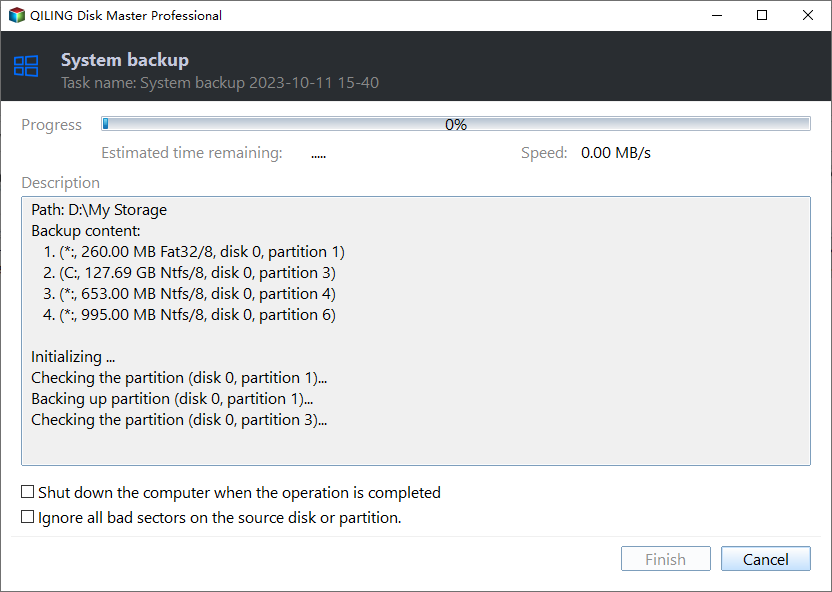
Step 4. Review the task summary and click "Proceed". Wait until the progress bar reaches 100%. Do not unplug the drive or turn off the PC while the backup is running.
Part 2: Restore Windows from the Backup
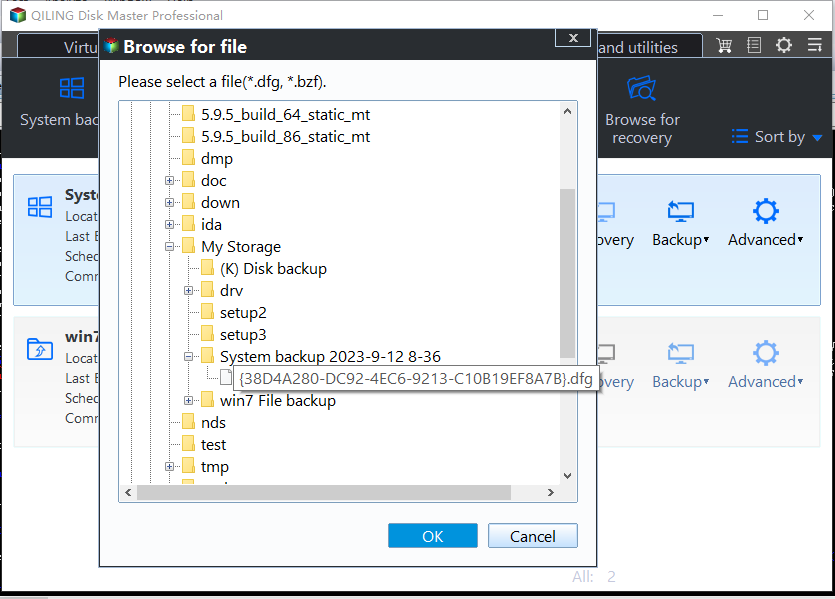
Step 1. Open Qiling Disk Master again, go to "Backup and Recovery", and select the recovery option. Your backup images are listed, so pick the one you created before you enabled Driver Verifier.
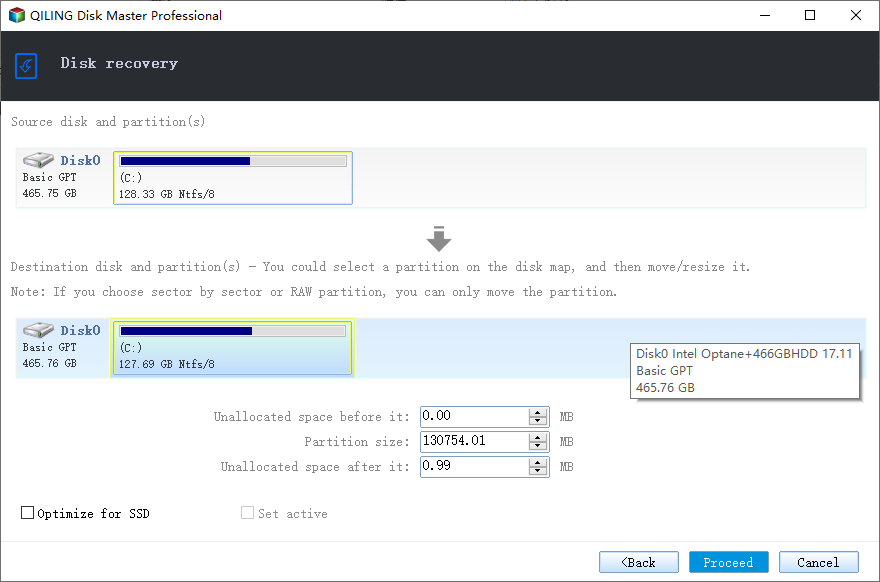
Step 2. Choose the target disk or partition. Normally you restore to the original system disk. If the drive was replaced, select the new disk instead, and the restore rebuilds Windows together with its boot partitions.
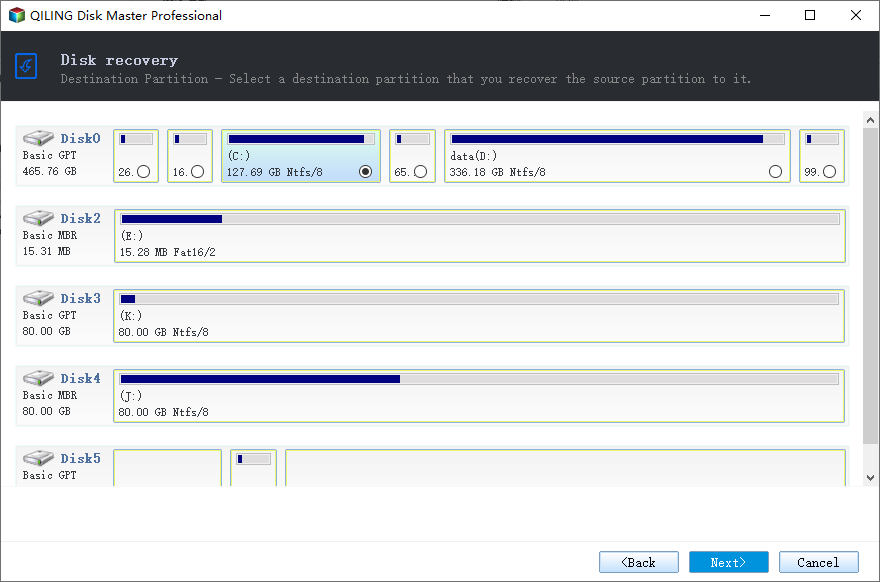
Step 3. Preview the restore plan, click "Proceed", and confirm the warning. The PC restarts to finish the job, and Windows comes back exactly as it was on the day the image was created, with your files and programs intact.
- Note
- Keep the backup image on a separate drive, and refresh it before every major change, such as enabling Driver Verifier, updating a driver, or changing firmware settings.
Conclusion
DRIVER_VERIFIER_DETECTED_VIOLATION means the kernel caught a driver breaking the rules while extra verification was active. Check whether you enabled Driver Verifier, and if you did, clear it with verifier /reset and verifier /bootmode resetonbootfail so the machine boots again. Then use Parameter 1 to understand the violation and the dump output to name the driver, and update, roll back, or remove that driver before re-testing.
Protect your PC with Qiling Backup—create a system image before your next troubleshooting step.
Related Articles
- Fix BAD_POOL_CALLER BSOD (0x000000C2)
BAD_POOL_CALLER is the other bug check that driver verification commonly reports. The two cover the same family of pool and IRQL mistakes. - Fix KMODE_EXCEPTION_NOT_HANDLED BSOD in Windows 11
- Fix UNEXPECTED_KERNEL_MODE_TRAP 0x0000007F in Windows 11
- BitLocker Recovery Key After a Windows Update
If the recovery environment asks for a key before you can run verifier /reset, this guide shows where the key is stored and how to retrieve it. - How to Fix the Windows 11 Blue Screen
Products
Articles & Tutorials
- Data Recovery
- Data Backup
- File Recovery
- File Backup
- System Backup and Restore
- Disk and Partition Clone
- Technical articles
- Mobile articles
- Disk Master Help
- Windows Data Recovery Tutorials
- Windows Secure Delete Tutorials
- Windows Partition Management Tutorials
- Windows File Backup and Restore Tutorials
- Windows System Backup and Restore Tutorials
- Windows Disk Backup and Restore Tutorials
- Windows Clone Tutorials