Windows 11 Secure Boot Certificate Expired in 2026 (Fix)
If you see a Secure Boot warning, or you read that Secure Boot certificates are expiring in 2026, do not panic and do not switch Secure Boot off. Your PC is not about to stop booting. What changes is how much protection the early boot stage receives from now on.
This guide explains what is actually expiring, how to check your own status in two minutes, and how to make sure your device receives the new 2023 certificates.
PAGE CONTENT
- What Is Happening with Secure Boot Certificates
- Does an Expired Certificate Stop Windows from Booting
- How to Check Your Secure Boot Certificate Status
- How Windows Delivers the New 2023 Certificates
- Install the New Certificates Step by Step
- If Windows Security Shows "Action Needed"
- What Not to Do When You See a Certificate Warning
- FAQs About Secure Boot Certificate Expiration
- Back Up and Restore Windows with Qiling Disk Master
What Is Happening with Secure Boot Certificates
Secure Boot works by checking the signature of early boot code against certificates stored in your firmware. The original certificates Microsoft issued in 2011 begin expiring in June 2026. Because those old certificates are still trusted by a huge number of motherboards, Microsoft is replacing them with a new set issued in 2023, commonly seen as "Windows UEFI CA 2023".
To make the change visible to ordinary users, the Windows Security app has shown the status of these certificate updates since April 2026, under Device security > Secure Boot. Three badge colours tell you where you stand:
- Green — the device has all required certificate updates and the updated boot manager is installed. Nothing to do.
- Yellow — an advisory. The device is still running on the older boot trust configuration and should receive updates, or a hardware or firmware limit is blocking them.
- Red — action needed. A boot security update cannot be delivered to the current boot configuration on this device.
The wording matters here. A green checkmark alone is not proof, so also look for the sentence "Secure Boot is on and all required certificate updates have been applied".
Does an Expired Certificate Stop Windows from Booting
No. This is the single most common misunderstanding, and it leads people to disable Secure Boot for no reason.
If your device never receives the newer 2023 certificates, the following still happen normally:
- The PC boots and Windows runs as usual
- Regular Windows Updates for apps, drivers, and features continue to install
- Your files, programs, and settings are unaffected
What you lose is narrower but still important. The device stops receiving new protections for the early boot process, including updates to Windows Boot Manager, updates to the Secure Boot databases and revocation lists, and mitigations for newly discovered boot-level vulnerabilities. Over time the boot chain falls behind current threat protection, and scenarios that depend on Secure Boot trust, such as BitLocker hardening or third-party bootloaders, can be affected.
- Note
- Think of it as an outdated antivirus definition file rather than a broken computer. Everything keeps working, but protection against newly discovered attacks stops improving until the certificates are updated.
How to Check Your Secure Boot Certificate Status
You have two simple checks. Use the first one for a quick answer and the second one if you want proof.
Step 1. Open the Windows Security app and go to Device security > Secure Boot. Read the coloured badge and the text under it.
Step 2. Open Settings > Windows Update > Update history, then expand Other updates. Look for an entry named "Secure Boot Allowed Signature Database (DB)" or similar.
Step 3. For a definitive answer, right-click Start, choose Terminal (Admin) or PowerShell (Admin), and run this command:
([System.Text.Encoding]::ASCII.GetString((Get-SecureBootUEFI db).Bytes) -match 'Windows UEFI CA 2023')
Step 4. If the result is True, the 2023 certificate is present in the Secure Boot database. If it is False, keep reading and apply the update steps below.
Step 5. If the command returns an error instead, Secure Boot is probably switched off in firmware. Check that first with msinfo32 and look at the "Secure Boot State" line.
How Windows Delivers the New 2023 Certificates
For most home and small business PCs, the new certificates arrive automatically and you do not need to do anything special.
- Through Windows Update. Microsoft updates the Secure Boot variables through the operating system, adding the 2023 certificates and, on newer builds, replacing older 2011-signed boot components with 2023-signed ones. The rollout has been staged since around May 2026.
- Through OEM firmware. Some machines need a UEFI or BIOS update from the manufacturer before the new certificates can be applied correctly. This is common on older laptops and on boards whose firmware stores default keys.
Two conditions must be met for the automatic path to work: the device must run a supported Windows version, and it must be receiving updates from Microsoft. Devices that are offline for long periods, or run an unsupported build, will not be updated.
Install the New Certificates Step by Step
Work through these steps in order. Most devices are fixed by step 2 or 3.
Step 1. Connect to the internet and go to Settings > Windows Update. Click "Check for updates" and install everything offered, including cumulative, servicing stack, and Safe OS or WinRE updates. Restart when asked.
Step 2. Visit your PC or motherboard manufacturer's support page and install the latest UEFI/BIOS firmware, especially if the release notes mention Secure Boot or certificate updates. Firmware refreshes the Secure Boot database and improves compatibility with the 2023 certificates.
Step 3. Restart the PC twice, not once. The database update is applied during boot, and a second restart makes sure the firmware has picked up the new variables.
Step 4. Run the PowerShell command from the previous section again and confirm it now returns True.
Step 5. If it is still False, open Task Scheduler, find the task under Microsoft > Windows > PI named Secure-Boot-Update, and run it manually, then restart twice and check again.
Step 6. If the certificate still does not appear and the manufacturer has released no firmware update, your device may be limited by its firmware. Keep Windows fully updated and check the Windows Security app for status changes, since Microsoft and its partners continue to refine the delivery path.
- Important
- Create a full system backup before flashing firmware or changing Secure Boot settings. Firmware operations are the one part of this process that can leave a PC unable to boot.
If Windows Security Shows "Action Needed"
A red badge is not a broken system. It means Windows detected that a boot security update cannot be delivered to your current boot configuration, which became possible once some 2011 certificates started expiring.
Step 1. Do not disable Secure Boot as a workaround. That removes the protection the update is trying to preserve.
Step 2. Install all pending Windows updates and the latest OEM firmware first, then restart twice and re-check the status.
Step 3. If your device is managed by a company, contact IT. Administrators have dedicated guidance for applying the new certificates through the operating system on validated hardware.
Step 4. If third-party bootloaders are in use, such as a custom Linux boot chain, check with that project for the 2023 certificate support before changing anything.
Step 5. If a "Secure Boot violation" message appears after the certificates update, boot from your Windows installation media and use the recovery options there to restore the boot configuration.
What Not to Do When You See a Certificate Warning
- Do not turn Secure Boot off. It is the most common reaction and the worst option, because it disables exactly the protection the certificate update exists to maintain.
- Do not reset Secure Boot to factory defaults unless your manufacturer's instructions say to. On many boards this can delete the 2023 keys that were already applied.
- Do not flash a BIOS from an unofficial source to chase a certificate. Use only the vendor's support page for your exact model.
- Do not ignore a red badge indefinitely. The PC will keep running, but its boot protection stops improving.
FAQs About Secure Boot Certificate Expiration
Will my PC stop booting in 2026?
No. Devices that do not receive the new certificates still boot and still install regular Windows updates. The change affects future boot-level security protections, not everyday operation.
Is Secure Boot itself expiring?
No. The older certificates signed in 2011 are expiring. Secure Boot as a feature continues to work, and Microsoft is replacing those certificates with a new set issued in 2023.
Do I need to update anything manually?
For most home PCs, no. Keep Windows Update enabled, install all updates, and apply any OEM firmware update that mentions Secure Boot or certificates. The rest is handled automatically.
What does the Windows Security badge mean?
Green means fully updated, yellow is an advisory about an older boot trust configuration, and red means an action is needed because a boot security update cannot be delivered to the current configuration.
Can I just disable Secure Boot to remove the warning?
You can, but you should not. Disabling Secure Boot removes the protection against boot-level malware and is explicitly discouraged by Microsoft as a workaround.
Why does the PowerShell command return False on my PC?
Either the 2023 certificate has not reached your device yet, or firmware limits are blocking it. Install or repair pending Windows updates, apply the latest OEM firmware, restart twice, and check again.
Back Up and Restore Windows with Qiling Disk Master
Before you flash a BIOS, change Secure Boot settings, or repair the boot configuration, create a full system backup. Firmware and boot changes are the operations most likely to leave a PC unable to start, and a system image is the fastest way back to a working state. Qiling Disk Master handles both the backup and the restore.
Part 1: Create a Full System Backup
Step 1. Install and open Qiling Disk Master. On the home screen, open "Backup and Recovery" and choose "System Backup". This option automatically includes Windows and the hidden boot partitions, so you do not have to select them one by one.
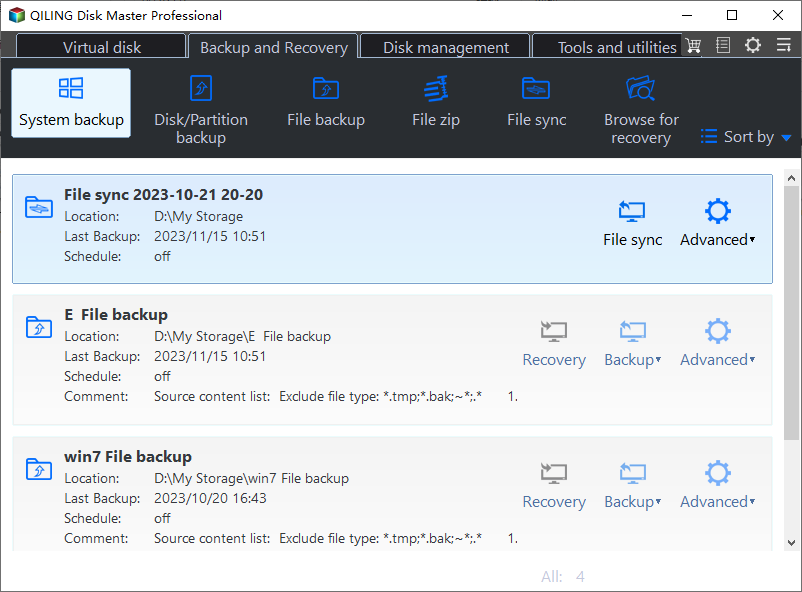
Step 2. Check the source. The disk where Windows is installed and its system partitions are already ticked for you. If you only need your personal documents, run a separate "File Backup" task instead.

Step 3. Click the destination box and choose where the image should be saved. Use an external HDD or SSD, a NAS, or any drive other than the one Windows is installed on, and make sure it has enough free space.
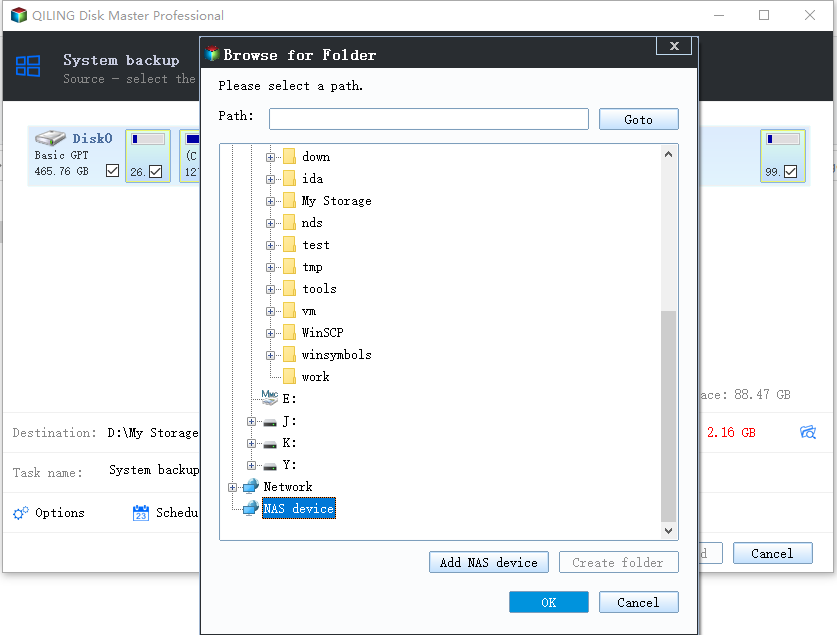
Step 4. Review the task summary and click "Proceed". Wait until the progress bar reaches 100%. Do not unplug the drive or turn off the PC while the backup is running.
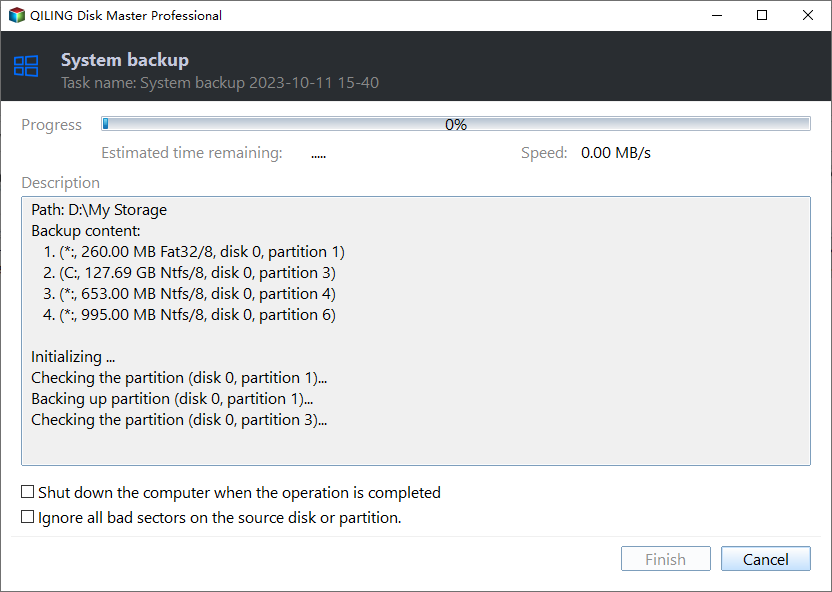
Part 2: Restore Windows from the Backup
Step 1. Open Qiling Disk Master again, go to "Backup and Recovery", and select the recovery option. Your backup images are listed, so pick the one you created before the firmware change.
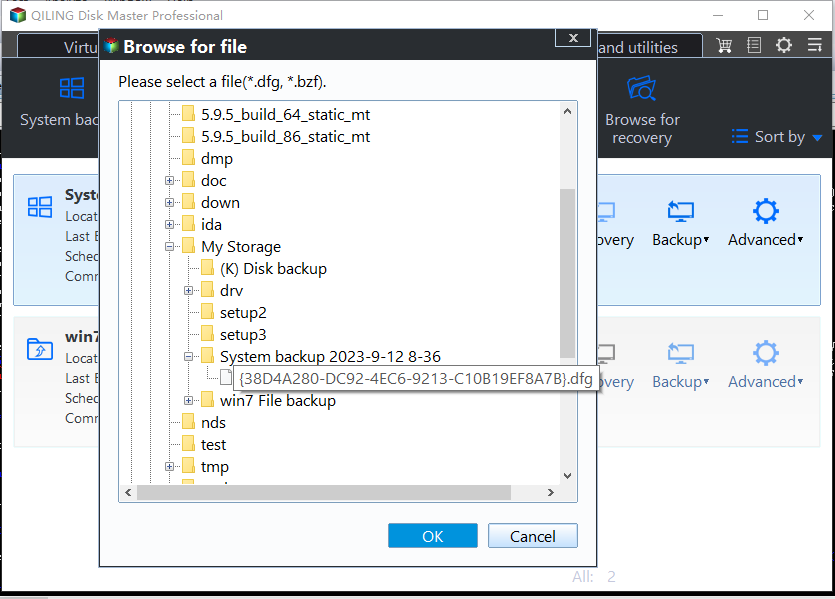
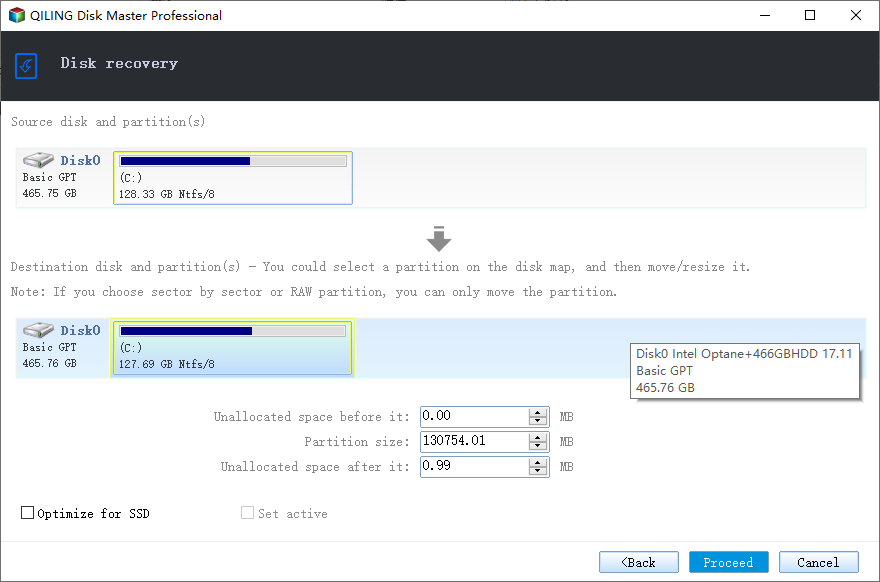
Step 2. Choose the target disk or partition. Normally you restore to the original system disk. If the drive was replaced, select the new disk instead, and the restore rebuilds Windows together with its boot partitions.
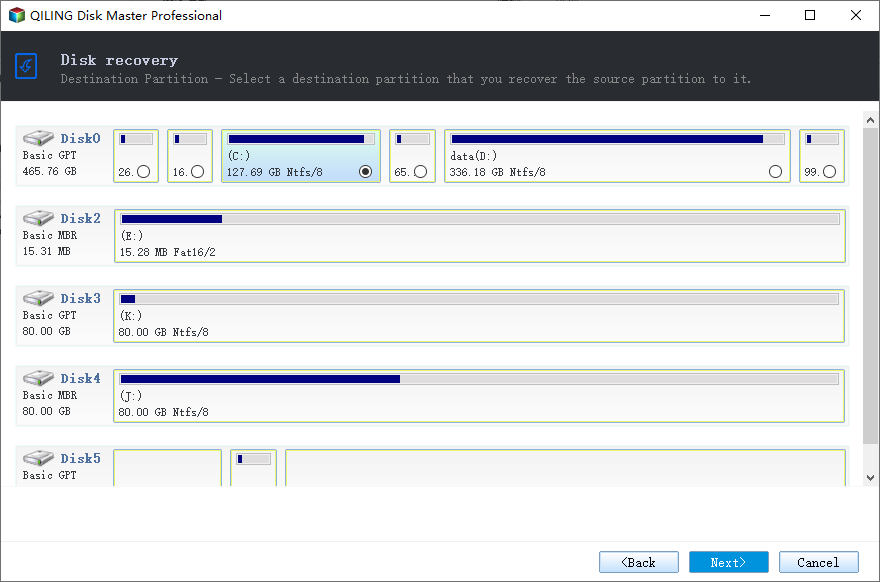
Step 3. Preview the restore plan, click "Proceed", and confirm the warning. The PC restarts to finish the job, and Windows comes back exactly as it was on the day the image was created, with your files and programs intact.
- Note
- Keep the backup image on a separate drive, and refresh it before every major change, such as a firmware flash, a Secure Boot change, or a Windows feature update.
Conclusion
Secure Boot certificates issued in 2011 start expiring in 2026, but the practical impact is smaller than the headlines suggest: your PC keeps booting, and regular Windows updates keep installing. What matters is making sure the new 2023 certificates reach your device. Open Windows Security to read your status, keep Windows Update fully patched, install the latest OEM firmware, restart twice, and confirm the result with the PowerShell check. Never disable Secure Boot to silence the warning.
Protect your PC with Qiling Backup—create a system image before your next firmware or boot change.
Related Articles
- How to Fix Secure Boot Violation on Windows 11
A Secure Boot violation usually appears after a boot configuration or firmware change. Learn what triggers it and how to recover without wiping your system. - Secure Boot Enabled but Not Active: How to Fix It
- How to Enable Secure Boot in Windows 11
- How to Repair the EFI Bootloader in Windows 11
If boot settings or firmware changes leave your PC unable to start, follow these steps to rebuild the EFI bootloader and get Windows loading again. - Windows 11 24H2 End of Support: What to Do Next (2026)
Products
Articles & Tutorials
- Data Recovery
- Data Backup
- File Recovery
- File Backup
- System Backup and Restore
- Disk and Partition Clone
- Technical articles
- Mobile articles
- Disk Master Help
- Windows Data Recovery Tutorials
- Windows Secure Delete Tutorials
- Windows Partition Management Tutorials
- Windows File Backup and Restore Tutorials
- Windows System Backup and Restore Tutorials
- Windows Disk Backup and Restore Tutorials
- Windows Clone Tutorials