How to Encrypt a Dual Boot Drive
A dual boot PC holds two operating systems on the same machine, often sharing a data drive between them. Encryption is important on such a setup, but it frustrates people when a protective step stops one of the systems from starting.
This guide shows how to encrypt a dual boot drive while keeping both systems able to boot and share files.
PAGE CONTENT
- Why Dual Boot Encryption Is Tricky
- What Works on a Shared Drive
- Encrypt a Shared Data Drive with Safe Disk
- Keep Both Systems Able to Boot
- Common Dual Boot Mistakes
- FAQs About Dual Boot Encryption
- Back Up Windows Before You Change Settings
Why Dual Boot Encryption Is Tricky
Full-disk encryption is tied to one operating system, which is exactly the problem on a shared machine.
- Boot loaders disagree. Each system uses its own boot process and may not read the other's encryption.
- Shared drives are common. A data partition used by both systems cannot belong to only one boot loader.
- Firmware gets involved. Some whole-disk methods depend on the hardware and BIOS settings.
- Updates disturb it. An update to one system can alter the boot order or the shared disk.
- One mistake locks you out. A wrong setting can leave both systems unable to start.
Windows-only whole-disk encryption rarely fits a machine that also runs Linux. For the system-disk case, see How to Encrypt Your Windows System Drive.
What Works on a Shared Drive
- A container is system-neutral. It is one file, so both systems can open it with the same password.
- No boot dependency. A container never touches the boot loader, so both systems still start.
- Selected files only. You protect the data you choose instead of the whole disk.
- Portable between systems. The container can be mounted from either system and moved freely.
- Safe to add later. It can be created on a drive that already holds files. See How to Encrypt a Second Internal Drive.
A container keeps the shared data protected without asking the boot loader to understand encryption.
Encrypt a Shared Data Drive with Safe Disk
Qiling Safe Disk protects files in a container, so neither system's boot process is affected. Download and install it first.
Step 1. Open Qiling Safe Disk and click Create to make a container on the shared drive.
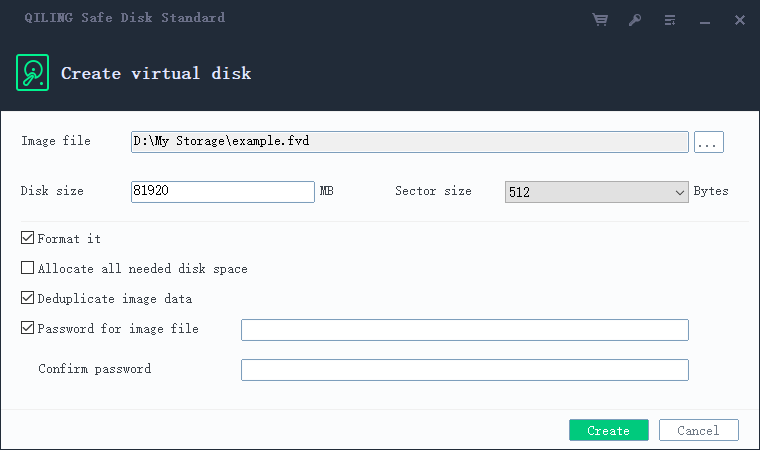
Step 2. Set a size, choose AES-256, and set a strong password.
Step 3. Mount the container and copy the files you want to protect inside it.
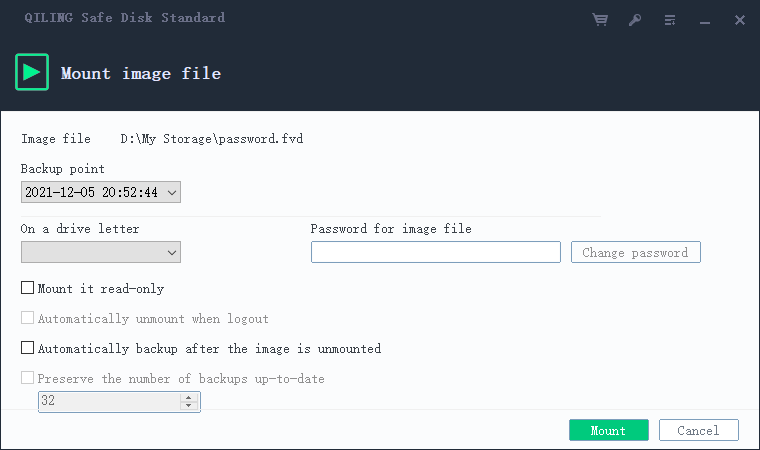
Step 4. Unmount whenever you switch systems so the container stays locked between them.
Keep Both Systems Able to Boot
- Leave the system disks alone. Encrypt the shared data, not the partitions that boot each system.
- Do not change boot order. A container never needs a boot loader entry, so leave the menu as it is.
- Test both systems. Reboot into each one and confirm both still start normally.
- Back up before you change. Keep an image of the boot partitions before any adjustment.
- Document the password. Both systems use the same container password, so it must be available.
The safest plan on a dual boot PC is to encrypt only the data you move between systems.
Common Dual Boot Mistakes
- Encrypting the wrong partition. Whole-disk tools may target a disk both systems rely on.
- Letting one system auto-repair. An update or repair can rewrite shared disk structures.
- Reusing a boot password. The container password should differ from either system's login.
- Skipping the backup. Changing disk settings without an image risks both systems at once.
- Forgetting to unmount. A container left open stays readable to whichever system is running.
Most dual boot failures come from touching the boot partitions. Protect your data and leave those alone.
FAQs About Dual Boot Encryption
Can I encrypt a drive shared by Windows and Linux?
Yes, if you use a container. A full-disk method tied to one system is far harder to share safely.
Will encryption stop either system from booting?
A container does not, because it never touches the boot loader. Whole-disk methods are the risky ones.
Do I need the same password on both systems?
For the shared container, yes, since both systems open the same file with one password.
What if one system cannot read the container?
Install the container software on that system, mount the file, and enter the password.
Is it better to encrypt each system separately?
That depends on your goal. Encrypting the shared data with a container protects the files both systems use.
Back Up Windows Before You Change Settings
Before installing security software or changing storage, create a full Windows backup. Qiling Disk Master creates a system image you can restore from.
Step 1. Open Qiling Disk Master and select System Backup to include Windows and the boot partitions.
Step 2. Save the image to a drive other than the Windows disk and start the backup.
Step 3. If a change causes issues, restore from the image to return Windows to its working state.
Conclusion
Encrypting a dual boot drive is easier when you protect the data instead of the boot process. A container is a single file, so both Windows and Linux can open it with the same password, and it never asks the boot loader to understand encryption. That keeps each system starting normally while the files they share stay scrambled when the container is closed. Create the container on the shared drive, move the sensitive files inside, and unmount it whenever you switch systems. Back up the boot partitions before any change, and keep the container password where both systems can rely on it. Qiling Safe Disk delivers this with AES-256 protection that follows the file wherever it goes.
For more on protecting drives that hold system data, see How to Create an Encrypted Virtual Drive, How to Encrypt a Drive Before PC Repair, Best Encrypted Virtual Drive Software for Windows, and How to Use Qiling Safe Disk.
Related Articles
- Encrypted Drive vs BitLocker: Which Should You Use?
Compare container encryption with full-disk encryption. - How to Encrypt an SSD
Protect a fast drive without slowing it down. - How to Encrypt an External Hard Drive
Add encryption to a drive that already holds files. - Does Encryption Slow Down Your Disk?
See how AES encryption affects real-world performance. - How to Mount an Encrypted Drive on Another Computer
Open a container safely from a different system.
Products
Articles & Tutorials
- Data Recovery
- Data Backup
- File Recovery
- File Backup
- System Backup and Restore
- Disk and Partition Clone
- Technical articles
- Mobile articles
- Disk Master Help
- Windows Data Recovery Tutorials
- Windows Secure Delete Tutorials
- Windows Partition Management Tutorials
- Windows File Backup and Restore Tutorials
- Windows System Backup and Restore Tutorials
- Windows Disk Backup and Restore Tutorials
- Windows Clone Tutorials