Fix ATTEMPTED_EXECUTE_OF_NOEXECUTE_MEMORY 0xFC in Windows 11
ATTEMPTED_EXECUTE_OF_NOEXECUTE_MEMORY, or stop code 0x000000FC, appears when the processor was told to run code stored at an address that Windows has marked as non-executable. In plain terms, the system jumped to a location it was never supposed to reach, and the hardware refused instead of running whatever bytes happened to sit there.
Unlike many stop codes, this one usually names its own culprit on screen. This guide explains what the message tells you, how to read the details, and how to fix the two realistic causes behind it.
PAGE CONTENT
- What the Stop Code Means
- Read the Crash Details Before Changing Anything
- Fix 1: Update or Clean-Install the Named Driver
- Fix 2: Test the Memory
- Fix 3: Remove Overclocking Instability
- Fix 4: Repair System Files and Check the Drive
- Fix 5: Firmware, Updates and a Malware Scan
- FAQs About Stop Code 0x000000FC
- Back Up and Restore Windows with Qiling Disk Master
What the Stop Code Means
Modern processors and Windows use data execution prevention, often called DEP or the NX bit. Memory pages that hold data are tagged as non-executable, so if the processor is ever asked to execute instructions from one of those pages, the hardware raises a fault. That mechanism exists to stop damaged or malicious code from running, and it also stops a corrupted program pointer from silently doing damage.
This stop code is that protection firing. It is not the corruption itself; it is the moment Windows caught it. Something reached an address it should never have reached, and only two realistic things cause that:
- A driver has a bug and calls a function pointer that is wrong, stale, or already freed
- The memory itself is unreliable, so a correct pointer was corrupted after it was written
Microsoft's own description is direct about the diagnosis: the guilty driver is on the stack trace and is typically the current instruction pointer, and when possible the driver's name is printed on the bug check screen and saved in a field called KiBugCheckDriver. That name is the single most useful clue you have.
- Note
- If the driver named on screen changes between crashes, suspect hardware such as the memory modules. If the same name appears again and again, suspect that driver first.
Read the Crash Details Before Changing Anything
Step 1. Look at the blue screen itself. Recent Windows 11 versions show a "What failed" line naming the driver or module that was running at the moment of the fault. Write that name down.
Step 2. Open the crash dump for more detail. A tool such as WinDbg, BlueScreenView, or WhoCrashed reads the files in the Windows Minidump folder and lists the modules involved in each crash. Run it on several dumps rather than one, so you can see whether a name repeats.
Step 3. Understand the parameters if you do open a debugger. The first argument is the virtual address that the processor was asked to execute, and the second is the contents of the page table entry for that address. The third and fourth arguments are reserved. You rarely need them for a repair; the module name matters more.
Step 4. Decide which path you are on. A single consistent driver points to a software fix. Several unrelated drivers, or a crash that repeats after you change nothing, points to the memory checks described below.
Fix 1: Update or Clean-Install the Named Driver
Step 1. Identify the category of the driver from its name or its folder. Graphics, network, audio, storage filter, virtualization, and security drivers are the usual offenders.
Step 2. For a graphics driver, do a clean install rather than an update. Remove the current driver with a display driver uninstaller while in Safe Mode, restart, and then install only the official package from the graphics vendor. Laptop owners should prefer the build published by the laptop maker, because it is validated for that chassis.
Step 3. For network, audio, or chipset drivers, download the package from the PC or motherboard maker instead of relying on a generic version.
Step 4. If the crashes began immediately after a driver or Windows update, roll that driver back in Device Manager and test again. A regression is far more common than a sudden hardware failure.
Step 5. Do not use automated driver updater utilities. They frequently install a newer but incorrect build and add a second variable you then have to rule out.
Fix 2: Test the Memory
Step 1. Run the built-in checker first. Press Windows and R, type mdsched.exe, and choose to restart and check now. The test runs before Windows starts, so save your work first.
Step 2. For a trustworthy result, follow up with a longer test. Windows Memory Diagnostic is quick but shallow; a bootable memory tester that runs four or more full passes, ideally overnight, catches faults the quick test misses.
Step 3. If any errors appear, reseat the memory modules, clean the contacts, and test one module at a time to isolate the faulty stick.
Step 4. Replace the faulty module. A single unreliable memory module is enough to produce this stop code repeatedly, and no software fix will compensate for it.
Fix 3: Remove Overclocking Instability
Step 1. Restart and enter BIOS or UEFI setup, then load the default or optimised settings.
Step 2. Disable the memory profile, whether it is labelled XMP or EXPO, and any manual processor or graphics overclock. These profiles push memory beyond the timings the platform guarantees, and an unstable profile produces exactly this pattern: a pointer that is correct when written but corrupted when read.
Step 3. Run the machine at stock settings for several days. If the crashes stop, reintroduce settings one at a time until you find the one that is not stable.
Step 4. On a laptop, also remove any undervolt or fan profile utility that changes power behaviour, since these are a common and easily overlooked source of instability.
Fix 4: Repair System Files and Check the Drive
Step 1. Open Command Prompt as administrator and repair the component store, then the protected system files:
DISM /Online /Cleanup-Image /RestoreHealth
sfc /scannow
Step 2. Restart even if the scan reports that it repaired files, because the replacement takes full effect only after a reboot.
Step 3. Check the health of the drive that holds Windows. A solid-state drive that is wearing out can return corrupted pages, and that corruption can reach a pointer. Use the drive maker's utility or a tool that reads the SMART attributes, and look at the reallocated sector count and the remaining life indicator.
Step 4. If the drive reports problems, back up your data immediately and plan a replacement. Do not wait for a second warning.
Fix 5: Firmware, Updates and a Malware Scan
Step 1. Update the system firmware. Check the PC or motherboard maker's support page for a BIOS or UEFI release newer than the one installed, then install the current chipset drivers.
Step 2. Install all pending Windows updates, including the optional driver updates offered under the advanced options.
Step 3. Run a full antivirus scan with an up-to-date definition set. Malicious kernel components are rare but not impossible, and a rootkit is one of the few things that can produce this stop code without a normal driver being at fault.
Step 4. Record what you changed. Because this stop code is often intermittent, a written log of each change makes it far easier to identify which one actually resolved it.
FAQs About Stop Code 0x000000FC
Is 0x000000FC always a hardware problem?
No. A buggy driver is the more common cause. Hardware becomes the leading suspect when several different drivers appear in the crash dumps or when the crash repeats without any software change.
The screen says "What failed: ntoskrnl.exe". Does that mean Windows itself is broken?
No. ntoskrnl.exe is the Windows kernel. It often appears simply because the kernel is where the fault was detected, while the real cause is a driver that called into it. Look lower down the stack in the dump for the third-party module.
Does DEP cause this error?
DEP, also called the NX bit, is what detects the violation by refusing to execute the page. It is the messenger, not the cause. Disabling it is not a fix and removes a meaningful protection.
Will resetting Windows fix it?
Only if the problem was a corrupted system file. A reset reinstalls the same drivers and does nothing about faulty memory or unstable firmware settings, so the crash usually returns.
Can uninstalling a program fix it?
Yes, if that program installed a driver. Antivirus suites, virtual private network clients, virtualization tools, disk encryption products, and storage utilities all install kernel drivers, and removing one is a valid test.
How do I know the problem is really fixed?
Run the machine normally for several days. This stop code tends to be intermittent, so a single successful boot proves very little. Stability over time is the real confirmation.
Back Up and Restore Windows with Qiling Disk Master
Driver and memory troubleshooting involves Safe Mode sessions, driver removals, and firmware changes, and any of those can leave a machine that will not start. Create a full system backup before you begin. Qiling Disk Master handles both the backup and the restore.
Part 1: Create a Full System Backup
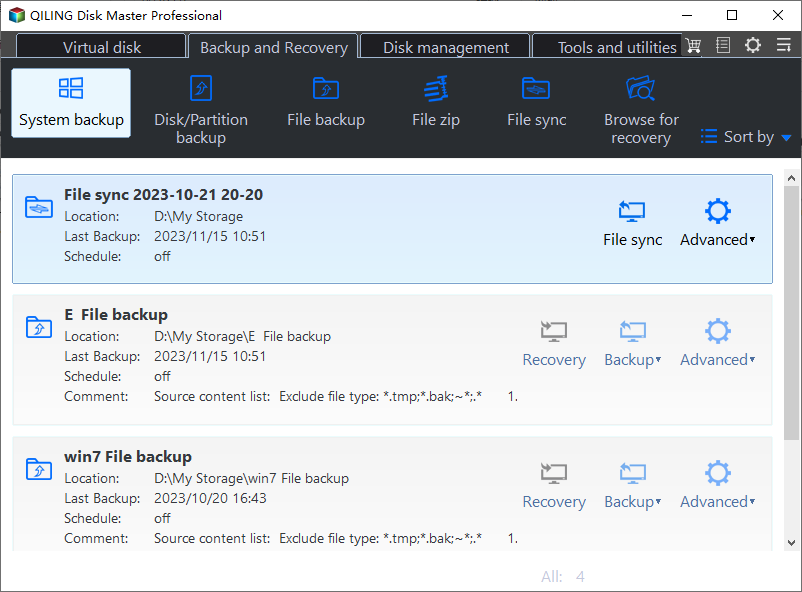
Step 1. Install and open Qiling Disk Master. On the home screen, open "Backup and Recovery" and choose "System Backup". This option automatically includes Windows and the hidden boot partitions, so you do not have to select them one by one.
Step 2. Check the source. The disk where Windows is installed and its system partitions are already ticked for you. If you only need your personal documents, run a separate "File Backup" task instead.

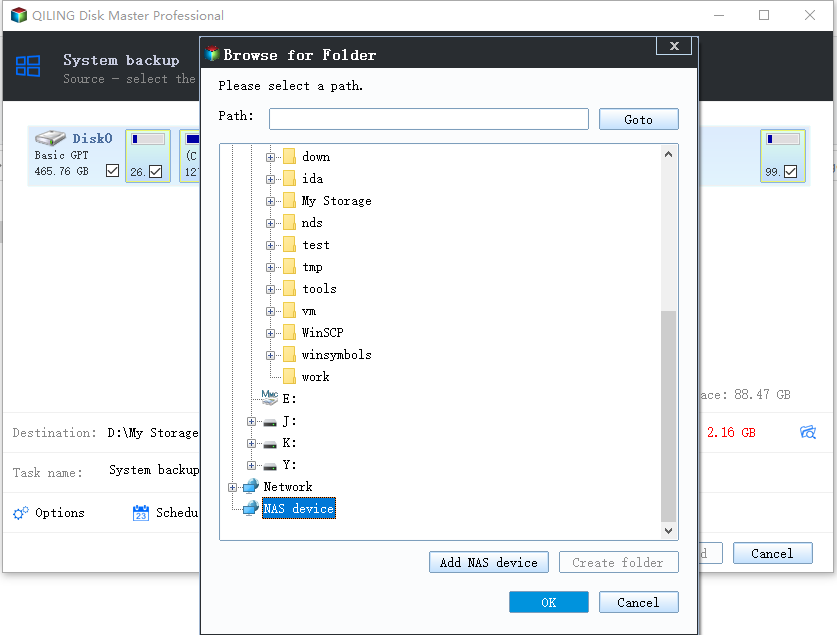
Step 3. Click the destination box and choose where the image should be saved. Use an external HDD or SSD, a NAS, or any drive other than the one Windows is installed on, and make sure it has enough free space.
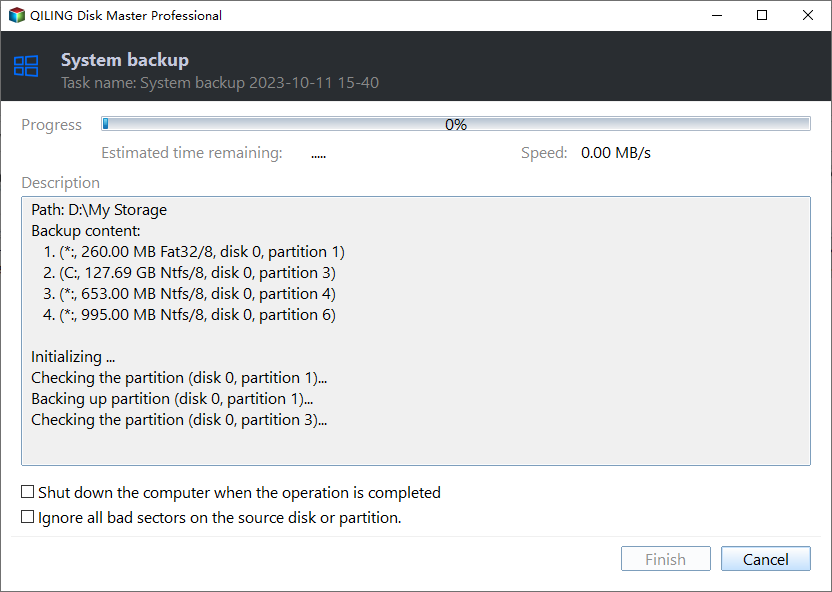
Step 4. Review the task summary and click "Proceed". Wait until the progress bar reaches 100%. Do not unplug the drive or turn off the PC while the backup is running.
Part 2: Restore Windows from the Backup
Step 1. Open Qiling Disk Master again, go to "Backup and Recovery", and select the recovery option. Your backup images are listed, so pick the one you created before the changes began.
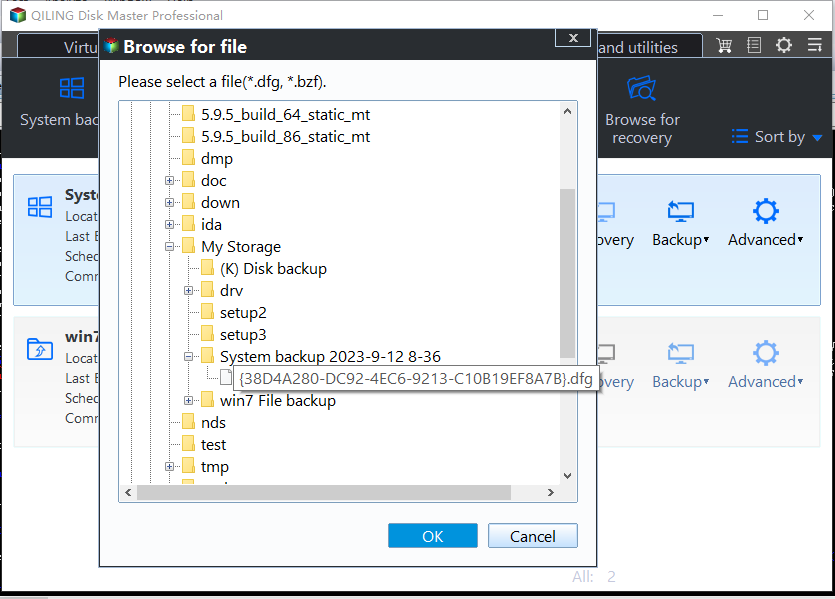
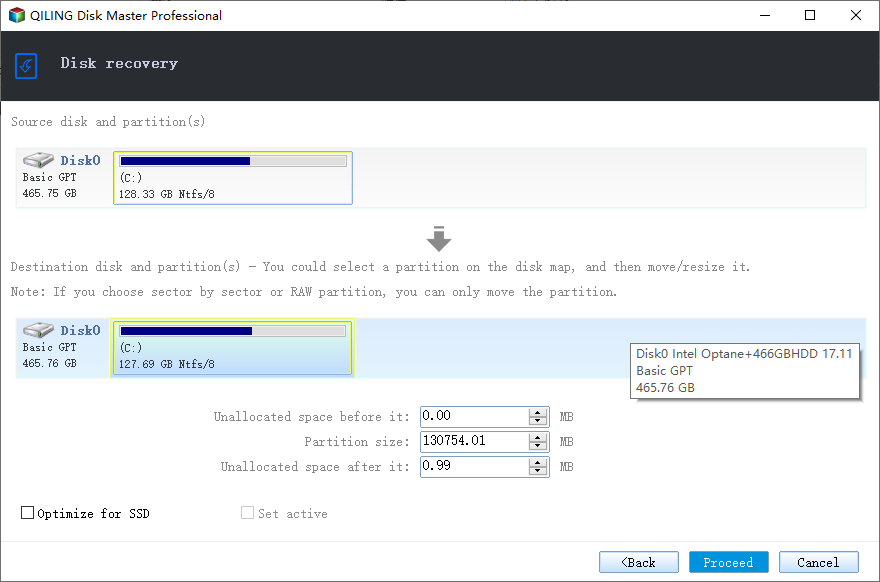
Step 2. Choose the target disk or partition. Normally you restore to the original system disk. If the drive was replaced, select the new disk instead, and the restore rebuilds Windows together with its boot partitions.
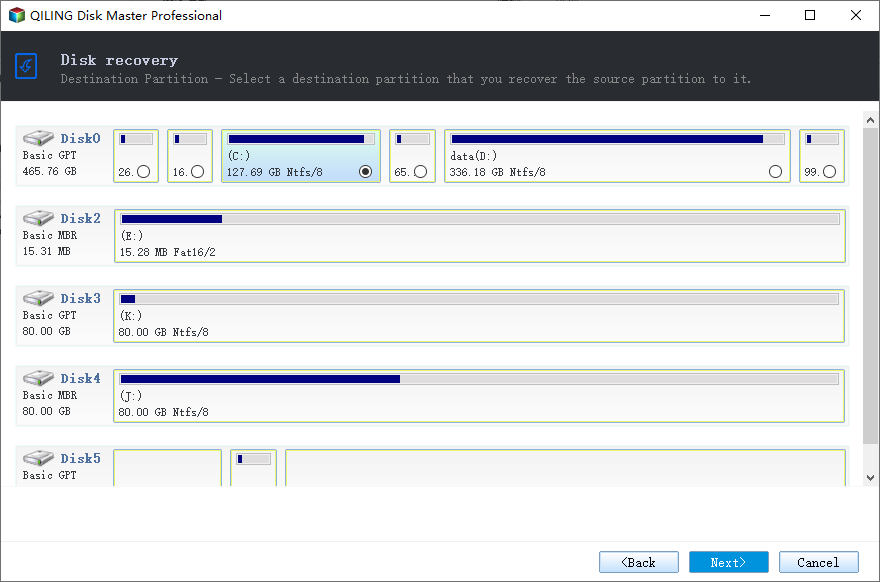
Step 3. Preview the restore plan, click "Proceed", and confirm the warning. The PC restarts to finish the job, and Windows comes back exactly as it was on the day the image was created, with your files and programs intact.
- Note
- Keep the backup image on a separate drive, and refresh it before every risky step, such as removing a kernel driver, changing memory timings, or updating the system firmware.
Conclusion
ATTEMPTED_EXECUTE_OF_NOEXECUTE_MEMORY means the processor was pointed at memory Windows had marked non-executable, and the protection layer stopped it. The stop screen usually names the driver responsible, so start there: update or clean-install that driver, and roll it back if the crashes began right after an update. If the named module changes between crashes, test the memory with a full pass of a bootable tester and remove any memory or processor overclock. Repair the system files, update the firmware, and confirm stability over several days rather than a single boot.
Protect your PC with Qiling Backup—create a system image before your next troubleshooting step.
Related Articles
- The PAGE_FAULT_IN_NONPAGED_AREA Error: Causes and Fixes
Both stop codes point at memory access that should never have happened. This article explains the page fault side of the same problem. - MEMORY_MANAGEMENT Blue Screen in Windows 11: How to Fix It
- Fix IRQL_NOT_LESS_OR_EQUAL BSOD in Windows 11
- Fix VIDEO_TDR_FAILURE BSOD in Windows 11
A graphics driver is one of the most frequent sources of non-executable memory faults. Check the driver stack when the named module is video related. - Windows 11 Blue Screen: Causes and Step-by-Step Fixes
- Fix DRIVER_OVERRAN_STACK_BUFFER (0xF7) in Windows 11
Products
Articles & Tutorials
- Data Recovery
- Data Backup
- File Recovery
- File Backup
- System Backup and Restore
- Disk and Partition Clone
- Technical articles
- Mobile articles
- Disk Master Help
- Windows Data Recovery Tutorials
- Windows Secure Delete Tutorials
- Windows Partition Management Tutorials
- Windows File Backup and Restore Tutorials
- Windows System Backup and Restore Tutorials
- Windows Disk Backup and Restore Tutorials
- Windows Clone Tutorials